Sovereign Cloud and Data Geopatriation Strategy
Sovereign cloud and data geopatriation strategy frameworks are rapidly becoming mandatory for enterprise leaders, cloud architects, and risk officers operating across the United States and European nations. For more than a decade, the overarching directive for corporate IT was simple: migrate every database, application, and analytics pipeline to global public hyperscale clouds. However, escalating geopolitical friction, international trade disputes, and conflicting cross-border privacy laws have shattered the illusion of a borderless digital ecosystem. Modern enterprises now recognize that placing all corporate data within foreign-incorporated public clouds creates unacceptable legal exposure and operational vulnerability.
Navigating this fragmented regulatory landscape requires a structured approach to digital autonomy, hardware isolation, and legal jurisdiction. By systematically categorizing workloads, deploying localized encryption controls, and establishing jurisdictionally compliant cloud tiers, multinational organizations can insulate their operations from foreign government subpoenas while preserving cloud agility. This strategy guide provides a comprehensive roadmap for implementing sovereign cloud architectures, navigating complex global data laws, protecting proprietary AI models, and executing risk-free data geopatriation projects.
Regulatory Drivers Shaping Sovereign Cloud and Data Geopatriation Strategy
Escalating legal conflicts between international jurisdictions are forcing global enterprises to re-evaluate where their digital assets physically reside. This section details jurisdictional crossfire, the EU AI Act, critical infrastructure compliance, and operational sovereignty guarantees.
Jurisdictional Conflicts Between US CLOUD Act and EU GDPR
Navigating conflicting extraterritorial laws represents the single largest regulatory hurdle for global enterprise IT architectures. The US CLOUD Act permits federal authorities to compel US-incorporated cloud providers to surrender customer data stored anywhere on earth, regardless of local regional privacy laws. Conversely, strict European privacy regulations like GDPR explicitly forbid unauthorized cross-border disclosures. This direct statutory conflict leaves global companies vulnerable to severe regulatory fines or severe legal sanctions unless workloads are decoupled from foreign jurisdiction.
EU AI Act Article 10 Data Governance Mandates
Complying with the enforcement of the EU AI Act requires rigorous data provenance and governance documentation for high-risk artificial intelligence applications. Article 10 mandates that datasets used to train, validate, and test enterprise AI models meet strict regional quality and bias standards. Storing sensitive training datasets on foreign public clouds exposes organizations to compliance audits and massive turnover-based penalties. Adopting local sovereign cloud infrastructure ensures that AI training data remains strictly within designated legal borders.
NIS2 Directive and DORA Critical Infrastructure Mandates
Implementing Europe’s NIS2 Directive and Digital Operational Resilience Act (DORA) expands strict cybersecurity obligations across financial institutions and critical services. These regulatory frameworks mandate direct oversight of third-party cloud supply chains and eliminate single points of failure. Enterprises must prove that critical operational software can run independently if access to foreign hyperscale clouds is suddenly severed or legally blocked. Establishing sovereign backup infrastructure provides guaranteed operational continuity during major international disruptions.
Operational Sovereignty and Foreign Personnel Access Restrictions
Achieving true operational sovereignty requires enforcing strict access controls that prevent foreign nationals from interacting with corporate infrastructure. Beyond physical data storage locations, operational sovereignty guarantees that cloud maintenance, system administrative access, and customer support engineers reside within the home legal jurisdiction. Restricting administrative access prevents foreign intelligence agencies from leveraging maintenance pathways to inspect sensitive enterprise databases or proprietary source code.
Architectural Models for Sovereign Cloud and Data Geopatriation Strategy
Designing a resilient sovereign cloud ecosystem requires moving away from monolithic, single-provider public cloud deployments. This segment examines three-tier workload architectures, region-scoped deployments, customer-managed encryption, and confidential computing environments.
Three-Tier Workload Architecture for Balanced Cloud Agility
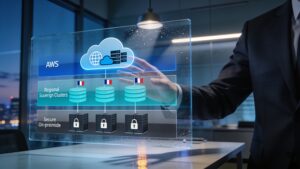
Implementing a three-tier workload model enables organizations to balance public cloud scalability with strict sovereign compliance. Under this model, public-facing non-sensitive applications run on public hyperscalers, while regional financial and operational data is isolated within local cloud providers. Core intellectual property, proprietary algorithms, and sensitive customer records are housed entirely within sovereign private clouds or on-premise datacenters. Tiered architecture prevents overall operational stagnation while securing core assets.
Region-Scoped Infrastructure and Strict Data Localization
Deploying region-scoped infrastructure stacks prevents accidental cross-border data leakage across automated backup pipelines and analytics feeds. Cloud architects isolate storage buckets, disable cross-region database replication, and deploy regional container clusters bound to specific physical zones. Enforcing strict regional tags at the infrastructure-as-code layer guarantees that sensitive database backups cannot automatically replicate into foreign data centers during routine failover procedures.
Customer-Managed Encryption Keys and Hardware Security Modules
Retaining sole custody of cryptographic keys ensures that data remains completely unreadable to cloud providers and foreign authorities. Utilizing dedicated Hardware Security Modules (HSMs) located physically on-premise guarantees that customer-managed encryption keys (CMEK) never leave corporate jurisdiction. Even if a public cloud provider is served a legal subpoena, they cannot decrypt the customer data hosted on their servers without access to the customer-held keys.
Confidential Computing and Trusted Execution Environments
Deploying Confidential Computing technologies protects active workloads in memory while data is undergoing computation. Hardware-based Trusted Execution Environments (TEEs) isolate processing memory from host operating systems, hypervisors, and cloud administrators. Encrypting data at rest, in transit, and during runtime eliminates exposure risks, allowing enterprises to process sensitive analytics or run AI inference on third-party cloud hardware securely.
Protecting AI Models and Corporate Data Through Model Sovereignty
The rapid adoption of enterprise generative AI has made training datasets and proprietary model weights the most valuable digital assets an organization owns. This section details model sovereignty, federated learning frameworks, localized inference, and policy-as-code enforcement.
Model Sovereignty and Proprietary Intellectual Property Shielding
Establishing model sovereignty ensures that proprietary neural networks and fine-tuned model weights remain fully protected under domestic law. Artificial intelligence models effectively act as compressed representations of the massive datasets used to train them. Exposing model weights to foreign public clouds risks unauthorized intellectual property exfiltration or forced legal disclosure. Securing AI models within sovereign boundaries shields core trade secrets and proprietary algorithms from foreign competitors.
Federated Learning and Decentralized Privacy-Preserving AI
Utilizing federated learning architecture allows organizations to train artificial intelligence algorithms across multiple geographical regions without moving raw data. Under this privacy-preserving model, local edge nodes compute model updates internally and transmit only encrypted parameter tweaks to a central server. Federated training satisfies strict local data residency requirements while enabling multinational enterprises to build highly accurate global machine learning models collaboratively.
Localized AI Inference Gateways and Runtime Policy Enforcement
Positioning localized AI gateway proxies between user applications and foundation models enforces real-time data loss prevention rules. AI gateways inspect incoming prompts and outgoing inference responses, automatically stripping personally identifiable information (PII) or confidential corporate data. Intercepting data streams at the local network perimeter guarantees that sensitive information is never accidentally passed to external cloud-hosted model endpoints.
Policy-as-Code and Automated Governance Pipelines
Integrating automated policy engines like Open Policy Agent into software deployment pipelines prevents compliance drift before code reaches production. Infrastructure-as-code scripts are automatically evaluated against data residency policies prior to deployment. Automated governance pipelines instantly block engineers from provisioning non-compliant cloud storage buckets or launching compute instances in unapproved geographical regions, enforcing continuous compliance across complex multi-cloud environments.
Operational Execution: Step-by-Step Data Geopatriation Roadmap
Executing a successful data geopatriation project requires methodical planning to avoid business disruptions and unnecessary CapEx spikes. This segment outlines inventory audits, provider evaluation, migration execution, and hybrid portability.
Comprehensive Data Categorization and Jurisdiction Auditing
Conducting a thorough data discovery audit is the foundational step of any geopatriation initiative. IT teams must catalog every corporate database, file share, and application workflow based on sensitivity and legal exposure. Classifying assets into clear tiers identifies which workloads can remain on cost-effective public clouds and which mission-critical databases require immediate relocation to domestic sovereign infrastructure.
Sovereign Cloud Provider Vetting and Legal Entity Inspection
Evaluating potential sovereign cloud partners requires looking far beyond physical server locations to inspect parent corporate structures. Organizations must verify that the cloud vendor is legally incorporated within their domestic jurisdiction and completely immune to foreign legal demands. Inspecting vendor ownership, administrative access policies, and certified security frameworks ensures the chosen infrastructure satisfies all legal operational sovereignty criteria.
Staged Workload Migration and Synthetic Stress Testing
Executing data geopatriation using a phased, iterative approach mitigates operational risks and prevents service downtime. System integrators build parallel sovereign environment staging stacks, running synthetic stress tests to validate performance, network latency, and database synchronization. Phased cutovers allow operations teams to verify data integrity and compliance posture before decommissioning legacy public cloud hosting instances.
Decoupled Identity Systems and Multi-Cloud Portability
Designing flexible multi-cloud architectures prevents vendor lock-in and ensures seamless future workload mobility. Decoupling identity and access management from proprietary cloud ecosystems allows organizations to manage access rights independently. Containerizing applications and using open-source orchestration tools ensures workloads can be moved rapidly between public hyperscalers, local sovereign clouds, or on-premise datacenters whenever regulations evolve.
Frequently Asked Questions (FAQ)
What is a sovereign cloud and data geopatriation strategy?
A sovereign cloud and data geopatriation strategy is a structured framework for moving sensitive data and AI workloads from foreign-controlled public clouds to local, jurisdictionally protected infrastructure to comply with regional privacy laws.
How does the US CLOUD Act impact European data hosted in EU datacenters?
The US CLOUD Act allows US authorities to compel American cloud providers to disclose customer data regardless of where servers are located, creating a legal conflict with European GDPR regulations unless data is hosted by a domestic sovereign provider.
What is the difference between data localization and data sovereignty?
Data localization simply requires that data be physically stored within a specific country’s borders, whereas data sovereignty ensures that the data is strictly governed by domestic laws and protected from foreign government subpoenas.
Can Confidential Computing replace the need for a sovereign cloud?
While Confidential Computing encrypts active data in memory during processing, it works best when combined with a sovereign cloud strategy to ensure both legal jurisdiction and operational hardware controls are maintained.
Final Conclusion
Developing an effective sovereign cloud and data geopatriation strategy is paramount for enterprise executives, risk officers, and technology leaders striving to maintain digital autonomy in a fragmented world. Moving away from total reliance on centralized public hyperscalers protects mission-critical data, proprietary AI models, and customer records from foreign legal interference. Adopting a balanced, three-tier cloud architecture allows organizations to combine public cloud performance with the uncompromised security of domestic sovereign infrastructure.
As data protection mandates like the EU AI Act, NIS2, and strict regional privacy laws expand across North America, Europe, and Asia, proactive compliance becomes a major competitive advantage. Investing in customer-managed encryption keys, confidential computing, and policy-as-code automation ensures enterprise systems remain compliant, resilient, and agile. Establishing clear digital sovereignty today safeguards corporate intellectual property and guarantees business continuity for years to come.
2 thoughts on “Sovereign Cloud and Data Geopatriation Strategy Guide 2026”